01 · Cybersecurity

AI did not invent the attack:
it removed its cost.

Attacks are now generated automatically; decisions about your company are not. We are an offensive-security and compliance team serving companies across Spain and abroad: we audit, explain and support, with a named analyst responsible for every project.

Barcelona · 41.39° N, 2.17° E · Spain and international

Manual pentestingWe exploit and demonstrate impact; we do not hand over a scanner report.
Retest includedWe verify the fixes in every audit.
One responsible analystWith a name, a phone number and availability on every project.

01 · The 2026 shift

The cost of attacking an SME is approaching zero

For two decades, attacking a Spanish SME took human time: writing a credible email, studying the org chart, impersonating a supplier. That cost was your best defence. It no longer is.

82,6 %of analysed phishing emails already contain AI-generated text 1
4,5×more clicks on AI-written phishing (54 % vs 12 %) 2
122.223incidents handled by INCIBE-CERT in Spain in 2025, 26 % more than in 2024 3

Vectors we audit in 2026

1 KnowBe4, Phishing Threat Trends Report 2025 · 2 Microsoft, Digital Defense Report 2025 · 3 INCIBE, Cybersecurity Report 2025.

02 · Services

Three service lines, one way of working

Scope in writing before we start, controlled execution and a report your team can act on without calling us. The budget is fixed after a thirty-minute scoping call.

01

Web, API and infrastructure pentesting

Manual offensive audit of the assets you expose and the ones that run the business: the application, the API behind it and the network it lives on.

For companies with their own application or client portal, e-commerce and SaaS, or that must evidence an audit to a large client, an insurer or a public tender.

What is included

  • Web application: authentication, session, access control, business logic and injection
  • REST or GraphQL API: object-level authorisation, rate limits and data exposure
  • External and internal infrastructure, Active Directory or cloud, per scope
  • Review of the organisation's credentials leaked in public sources
  • Technical report with proof of concept and CVSS score, executive summary and prioritised plan
  • Verification retest included

What is not included

  • Continuous red team or multi-month campaigns, quoted separately
  • Full source-code audit, which can be added to the scope
  • Attacks with denial-of-service risk, unless expressly authorised

Half of the serious findings we identify are invisible to tools: they are business-logic and permission flaws.
02

vCISO, security leadership on a monthly fee

A security lead for companies that need judgement and governance but cannot justify a full-time CISO.

For companies of up to 250 employees that are asked for a security questionnaire to act as a supplier, must prepare GDPR compliance, or whose management needs to know the risk it is carrying.

What is included

  • Risk analysis and twelve-month roadmap, prioritised by impact and cost
  • Policies and procedures: security, access, backups and incident response
  • Compliance preparation: GDPR, and anticipation of DORA and CRA
  • Vendor management: questionnaires, clauses and third-party assessment
  • Regular security committee and reporting to management in business language
  • Incident response and support, including notification to the data-protection authority where required

What is not included

  • 24/7 SOC operation, integrated with a specialised provider if needed
  • Day-to-day systems administration

Monthly fee with an annual commitment, committed hours and one fixed contact from start to finish.

03

AI and agent audit, plus anti-deepfake protocol

Your company has connected an assistant to the catalogue, an agent to email or a copilot to the ERP. We test what that agent can do when someone deliberately manipulates it.

For companies that have integrated language models, agents or automations with access to real data or actions, and executives exposed to voice-cloning fraud.

What is included

  • Direct and indirect prompt injection, using documents, websites and emails as the vector
  • Agent permissions and credential scope: what it can read, write and execute
  • Exposure of MCP servers and connected tools
  • Data leakage through integrations, context and logs
  • RAG source poisoning and knowledge-base manipulation
  • CEO-fraud protocol and AI-generated phishing simulation

What is not included

  • Model bias or quality audit, which is not offensive security
  • Formal AI Act certification: we prepare the file, we do not certify

Methodology based on the OWASP Top 10 for LLM applications.

03 · How we work

Five phases, no surprises and no impact on production

The same methodology on every engagement, aligned with OWASP WSTG and executed under control. Everything is in writing before any test starts.

1

Scope and rules of engagement

Assets, time windows, authorised techniques, emergency contacts and stop criteria. Signed before we start, together with the NDA.

Signed rules of engagement
2

Reconnaissance

Exposed surface, subdomains, services, technologies and public credential leaks of the organisation.

Attack-surface map
3

Identification

Tools and manual work. Automation covers volume; business logic, permissions and authorisation flows are tested by hand.

Findings inventory with CVSS
4

Controlled exploitation

We confirm real impact without exfiltrating data or degrading service. On a critical finding, we inform you the same day.

Proof of concept per finding
5

Report and retest

Technical report, executive summary and prioritised plan. Presentation meeting and retest window included.

Report and retest record

04 · Who we are

A specialised team, no intermediate layers

METROPOLI BCN SL is a cybersecurity consultancy serving companies across Spain and abroad. The person who defines the project is the one who delivers it and who informs you when a critical finding appears.

Real offensive capability

Manual pentesting of web, API and infrastructure. We do not hand over a scanner report: we exploit, demonstrate impact and document it with a reproducible proof of concept.

Compliance you can understand

GDPR and preparation for DORA, CRA and the AI Act. We turn every legal requirement into a task plan with an owner and a date.

An assigned analyst

Every project has a responsible analyst with a name, a phone number and availability. No call centre, no intermediate escalation levels.

Nationwide and beyond

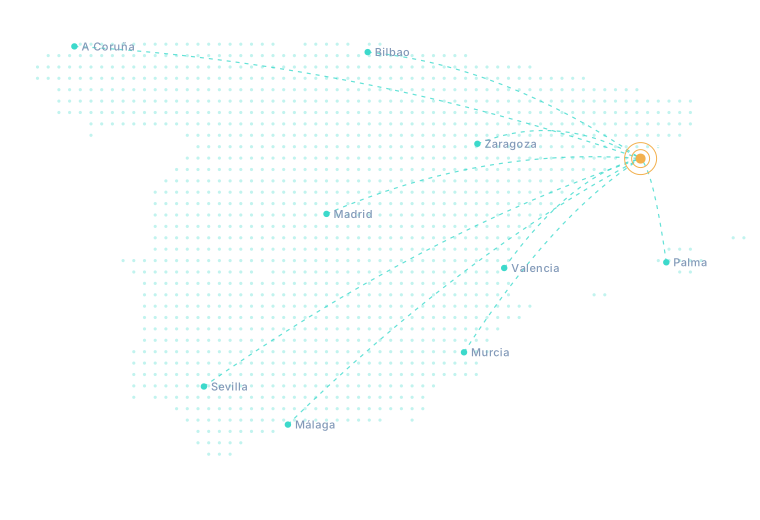
We serve companies across Spain and abroad. Audits run remotely by nature; on-site sessions are agreed per project.

Coverage

From Barcelona, for all of Spain and worldwide

Audits run remotely by nature. On-site sessions with management are agreed per project, in any city.

Head office
El Masnou (Barcelona)
Scope
All of Spain and worldwide
Languages
Spanish, Catalan, English, German
Mapa de España con nodos de servicio conectados a Barcelona

The usual alternatives and how they differ

Your regular IT providerKnows the network and keeps it running, but does not run offensive tests or write reports with evidentiary value.
Large MSSPHas capacity and 24/7 coverage; attention is spread across hundreds of clients and the contact changes.
Automated platformDetects known vulnerabilities cheaply; the application's business logic is out of its reach.
METROPOLI BCNThe same person defines the scope, performs the exploitation and informs you when a critical finding appears.

What we do not do

We do not resell licences or take vendor commissions: our recommendation is independent.
We do not run our own 24/7 SOC; when needed, we integrate a third-party provider and supervise it.
We do not sign reports for work we have not performed ourselves, nor do we subcontract audits.
We do not accept engagements we cannot deliver to a high standard within the agreed timeframe.

05 · Regulatory calendar

What applies to you, and when

Only what is published in the Official Journal. Our job is to determine what really applies to you and get the preparation done ahead of time.

2025202620272028TODAYDORAApplicableAI ActTransparency (art. 50)CRAVulnerability reportingCRA · full applicationAI · high risk (Annex III)AI ActHigh risk (Annex I)
  1. 17 Jan 2025DORAAplicable
  2. 2 Aug 2026AI ActTransparencia (art. 50)
  3. 11 Sep 2026CRANotificación de vulnerabilidades
  4. 2 Dec 2027AI ActAlto riesgo (anexo III)
  5. 11 Dec 2027CRAAplicación plena
  6. 2 Aug 2028AI ActAlto riesgo (anexo I)
GDPRIn forceYou process personal data (almost every company). In force; fines of up to €20 M or 4 % of turnover.
ENS · RD 311/2022In forceSpanish public-sector security scheme: applies if you bid for or supply Spanish public bodies. In force; certification is required to tender.
DORA · (EU) 2022/2554In forceYou invoice banks, insurers or fintechs, or provide them ICT services. Applicable since 17/01/2025; it reaches you by contract even if you are not a regulated entity.
AI Act · (EU) 2024/1689PartialYou develop or integrate AI systems or agents. Transparency (art. 50) from 02/08/2026; high-risk from 02/12/2027 (Annex III) and 02/08/2028 (Annex I), per Regulation (EU) 2026/1744.
Cyber Resilience Act · (EU) 2024/2847PartialYou sell software or connected devices. Vulnerability reporting from 11/09/2026; full application on 11/12/2027.
NIS2 · (EU) 2022/2555PendingEssential or important entity in a critical sector. Transposition varies by member state; the directive's obligations are the working reference.

06 · Contact

Thirty minutes to find out what you really need

The initial call is free and includes no sales pitch. You describe what you expose; we tell you what we would audit first and with what budget, even if the conclusion is that you do not need it yet.

  1. Thirty-minute scoping call
  2. Fixed proposal within 48 hours, with scope and schedule
  3. Signing of rules of engagement and NDA, and start date
→

When you write to us, we process your contact details only to handle your request, as set out in our privacy policy.

Company
METROPOLI BCN SL
Tax ID
B65272791
Registered office
C/ Àngel Guimerà, 19, bajos, 08320 El Masnou (Barcelona), España
Scope
All of Spain and abroad, remote and on site per project

Frequently asked questions

Confidentiality
We sign an NDA before receiving any information, together with a GDPR Article 28 processor agreement.
Evidence
Seen only by the assigned analyst and a second internal reviewer. Encrypted, hosted in the EU and deleted after 90 days.
Frequency
Once a year as a rule, and always after a relevant change: new critical functionality, a migration or an agent integration.